Play Intro
AboutExperienceProjectsCapabilitiesContactResume ↗
Open to Azure Cloud Roles · Bengaluru

Cloud that
you need
secured.

Building secure Azure environments with IaC, CI/CD pipelines, and cloud security. Microsoft AZ-900 Certified.

Scroll downto see projects
ForeScout NAC
Cisco ISE
802.1x / MAB
RADIUS
Azure VNet
NSG Hardening
RBAC Governance
Log Analytics
KQL Queries
Microsoft Defender
Terraform
GitHub Actions
CI/CD Pipeline
Active Directory
WAF · SSLO
ForeScout NAC
Cisco ISE
802.1x / MAB
RADIUS
Azure VNet
NSG Hardening
RBAC Governance
Log Analytics
KQL Queries
Microsoft Defender
Terraform
GitHub Actions
CI/CD Pipeline
Active Directory
WAF · SSLO
About me

Meet
Prasanth.

I'm a Network Security Engineer at NTT India Private Limited, currently working on NAC L1 Support at Indian Bank HQ under Managed Services. With a strong foundation in Azure cloud security and infrastructure, I bring hands-on experience in network access control, endpoint compliance, and enterprise security operations.

I hold a Post Graduate Diploma in Cloud Data Management from Conestoga College, Canada, and have built two enterprise Azure projects covering secure networking, NSG hardening, KQL monitoring, RBAC governance, and CI/CD automation — skills that directly complement my work in network security and infrastructure.

Network SecurityNAC (ForeScout)Cisco ISE802.1x / MABAzure CloudCloud SecurityLog AnalyticsKQLRBAC & IAMAzure PolicyTerraformGitHub Actions
Network Security Engineer (NAC L1)NTT India · Indian Bank HQJune 2026 – Present
PG Diploma – Cloud Data MgmtConestoga College, Canada2025
B.E. Computer ScienceKumaraguru College of Technology2023
Prasanth Panneer Selvam
Network Security Engineer · NTT DATA
LinkedIn ↗GitHub ↗
Experience
NTT DATA
Network Security Engineer (NAC L1 Support)
NTT India Private Limited · Full-time
June 2026 – Present · Chennai, India
Current Role

Working as an L1 Network Access Control (NAC) support engineer at Indian Bank HQ under NTT India Managed Services, responsible for monitoring and maintaining enterprise network security infrastructure for 79,000+ endpoints across Indian Bank branches nationwide using ForeScout NAC solution.

Monitor and manage network access for 79,000+ endpoints across Indian Bank branches using ForeScout Enterprise Manager console
Troubleshoot 802.1x and MAB authentication failures for Windows and IoT devices including ATMs, printers, biometric systems, and VOIP phones
Manage MAC Address Repository (MAR) whitelisting for IoT device onboarding and analyze RADIUS authentication status and compliance posture
Work with Cisco, Aruba, and Tejas switches using CLI commands via Putty to diagnose port-level connectivity issues
Coordinate with L2 teams for domain rejoin, OS-related, and credential guard issues via ITSM ticketing system
Ensure endpoint compliance with Trend Micro Antivirus, Forcepoint DLP, Radia Patch, ForeScout Agent, and Titus data classification
Monitor network security components including WAF, SSLO, AAA (Cisco ISE), and Server Load Balancer
ForeScout NAC v8.5Cisco ISE v3.4802.1x / PEAPMABRADIUSActive DirectoryCisco SwitchesAruba SwitchesTejas SwitchesPuttyWAFSSLOSLBITSM
Recent Works
All Projects ↗
CloudGuard
View on GitHub ↗
CloudGuard
Azure Secure Cloud Infrastructure · 6 Phases
▶ terraform apply
azurerm_resource_group.rg: Creating...
azurerm_virtual_network.vnet: Creating...
azurerm_subnet.public: Creating...
azurerm_network_security_group.nsg: Creating...
Apply complete! 5 resources added.
✓ GitHub Actions CI/CD
✓ Terraform IaC
✓ Azure VNet + NSG
View on GitHub ↗
CloudGuard IaC Pipeline
Terraform + GitHub Actions CI/CD · Auto Deploy
Capabilities

What I build & protect

From enterprise network access control and endpoint compliance to Azure cloud security and infrastructure automation — bridging network security and cloud engineering.

0+
Endpoints managed
0
Cloud certifications
AZ-900
Microsoft certified
🛡️
Network Access Control
ForeScout NAC, 802.1x/MAB authentication, RADIUS, MAC Address Repository, endpoint onboarding and compliance posture management.
🔒
Cloud Security
NSG hardening, Microsoft Defender for Cloud, Zero-Trust principles, threat detection and response on Azure environments.
🌐
Network Infrastructure
Cisco, Aruba, and Tejas switch management via CLI, port-level diagnostics, VLAN configuration, and connectivity troubleshooting.
📊
Monitoring & KQL
Log Analytics Workspace, custom KQL queries, Azure Monitor alerts, WAF/SSLO/SLB monitoring and security event analysis.
🏛️
Governance & Policy
Azure Policy enforcement, compliance scoring, resource tagging, RBAC role assignments, and endpoint compliance enforcement.
⚙️
Infrastructure as Code
Terraform provisioning, GitHub Actions CI/CD, GitOps workflows, and automated Azure infrastructure deployment.
Azure Virtual NetworkNetwork Security GroupsAzure FirewallRBAC & IAMMicrosoft Defender for CloudLog Analytics WorkspaceKQLAzure MonitorTerraformGitHub ActionsAzure Virtual NetworkNetwork Security GroupsAzure FirewallRBAC & IAMMicrosoft Defender for CloudLog Analytics WorkspaceKQLAzure MonitorTerraformGitHub Actions
ForeScout NACCisco ISE802.1xRADIUSActive DirectoryAruba SwitchesCisco SwitchesAzure PolicyAZ-900AWS CCPCI/CD PipelineWAFSSLOITSMForeScout NACCisco ISE802.1xRADIUSActive DirectoryAruba SwitchesCisco SwitchesAzure PolicyAZ-900AWS CCPCI/CD PipelineWAFSSLOITSM
$
How I work

Process

Hover over each phase to explore. 8 structured phases across 2 projects building a complete enterprise Azure security environment.

View CloudGuardSee Projects
01
🏗️
Infrastructure Setup
Built VNet with public/private subnets, Storage Account, and Log Analytics Workspace from scratch on Azure Portal.
02
🔒
Network Security
Configured NSG inbound rules with IP whitelisting (/32 CIDR), attached to private subnet, validated logs with KQL.
03
📊
Security Monitoring & Log Analytics
Deployed dedicated Log Analytics Workspace, streamed Activity Logs, ran KQL queries to detect failed operations.
04
🚨
Alerting & Incident Notifications
Set up Azure Monitor Alert Rules targeting admin error events with Action Groups for automated email notifications.
05
🛡️
Security & Governance
Created custom RBAC role with least-privilege permissions and enforced mandatory resource tagging via Azure Policy.
06
🔍
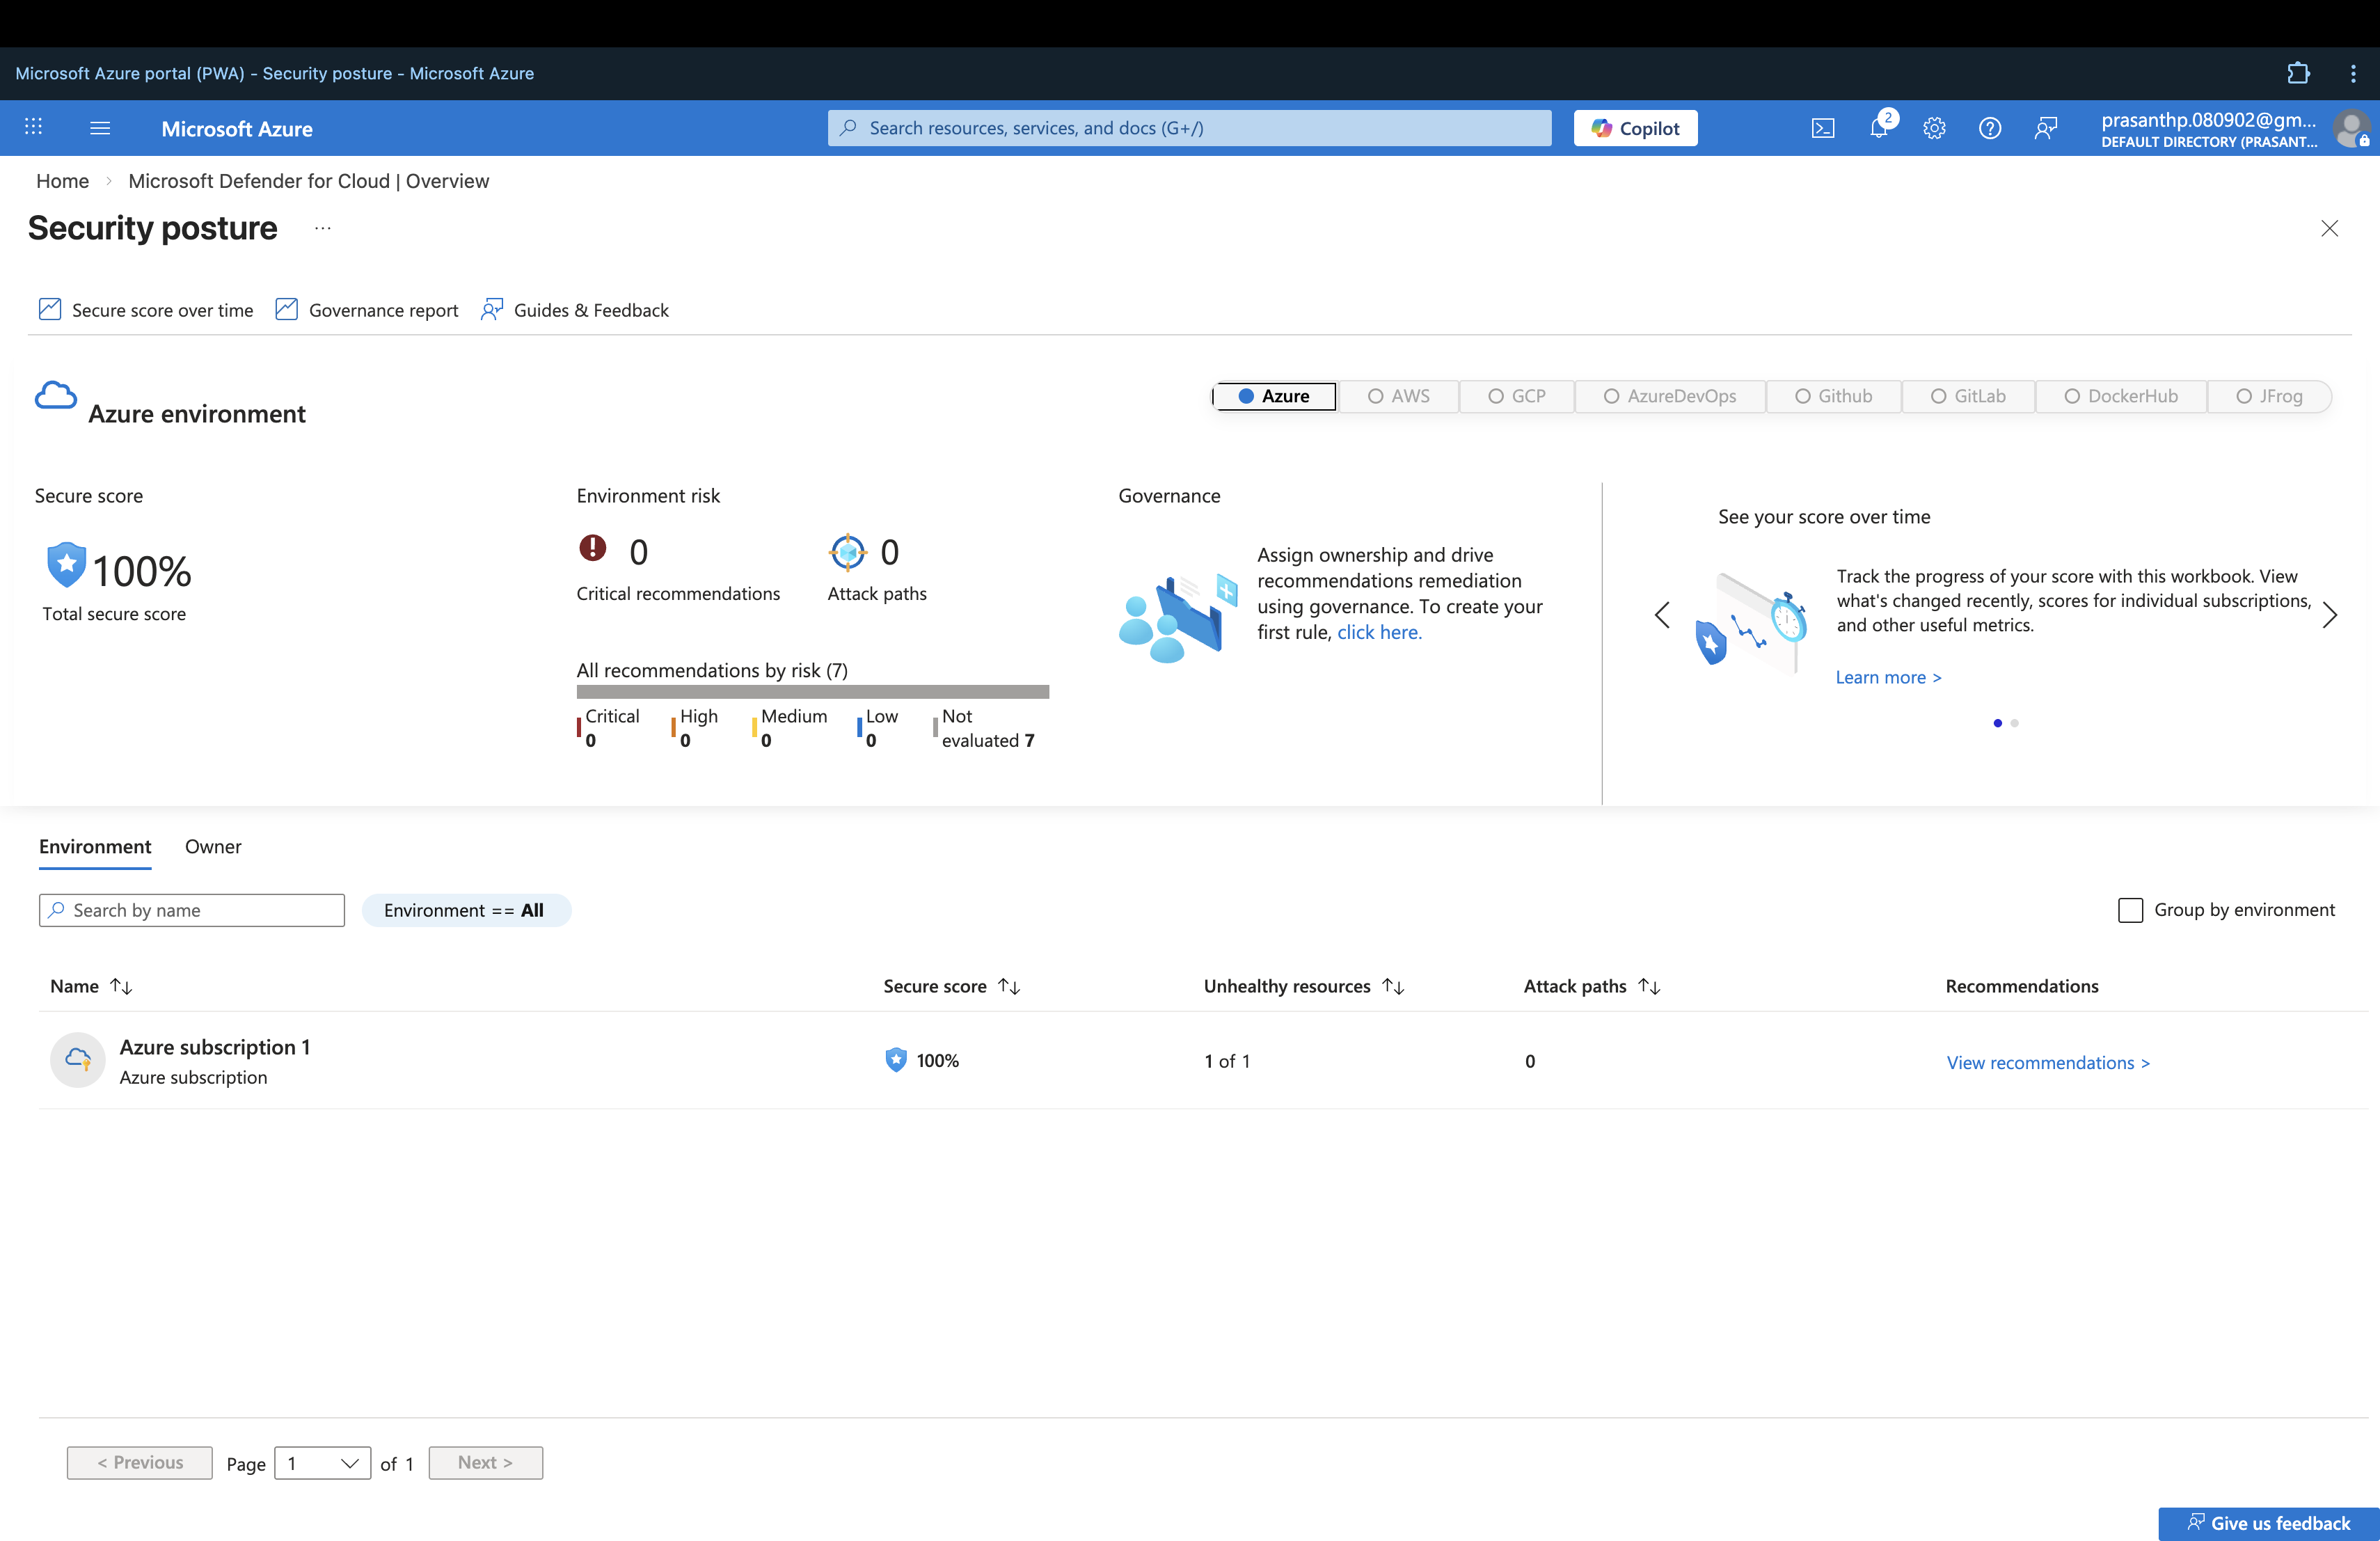
Defender for Cloud
Assessed Secure Score, investigated security recommendations, and mapped controls to Azure Security Benchmark.
07
⚙️
Infrastructure as Code
Wrote Terraform configs (main.tf, vnet.tf, nsg.tf) to provision Azure Resource Group, VNet, subnets, and NSG — no manual portal clicks.
08
🔄
CI/CD Pipeline Automation
Built GitHub Actions workflow triggering on every push — runs terraform init, plan, and apply automatically to Azure.
Offer Received · NTT DATA 🎉

Time without
1st job offer.

0
Hours
0
Minutes
0
Seconds

🎯 Timer stopped. The owner landed his first job.

FAQ
Answers.

Common questions about my background, current role, and how to get in touch.

I am a Network Security Engineer (NAC L1 Support) at NTT India Private Limited, deployed at Indian Bank HQ under Managed Services. I monitor and maintain network security infrastructure using ForeScout NAC and Cisco ISE.
Microsoft Certified: Azure Fundamentals (AZ-900) and AWS Certified Cloud Practitioner (AWS CCP). Currently targeting AZ-104 as the next milestone.
CloudGuard is my enterprise-grade Azure project covering 6 phases: secure networking, NSG hardening, Log Analytics monitoring with KQL, automated alerting, custom RBAC governance, Azure Policy, and Microsoft Defender for Cloud.
CloudGuard IaC Pipeline is my second Azure project — it automates the entire infrastructure deployment using Terraform and GitHub Actions CI/CD. Every push to GitHub triggers an automated pipeline that provisions Azure VNet, subnets, and NSG — eliminating manual portal clicks.
ForeScout NAC, Cisco ISE (AAA), 802.1x/MAB authentication, RADIUS, Active Directory, Cisco/Aruba/Tejas switches, WAF, SSLO, and ITSM ticketing. On the cloud side: Azure, Terraform, GitHub Actions, KQL, and Microsoft Defender for Cloud.
Email me at prasanthp.080902@gmail.com or connect on LinkedIn at linkedin.com/in/prasanthpanneer. I typically respond within 24 hours.
Available for Work

Curious about what we can build together? Let's make it happen.